Loading project concept…
All projects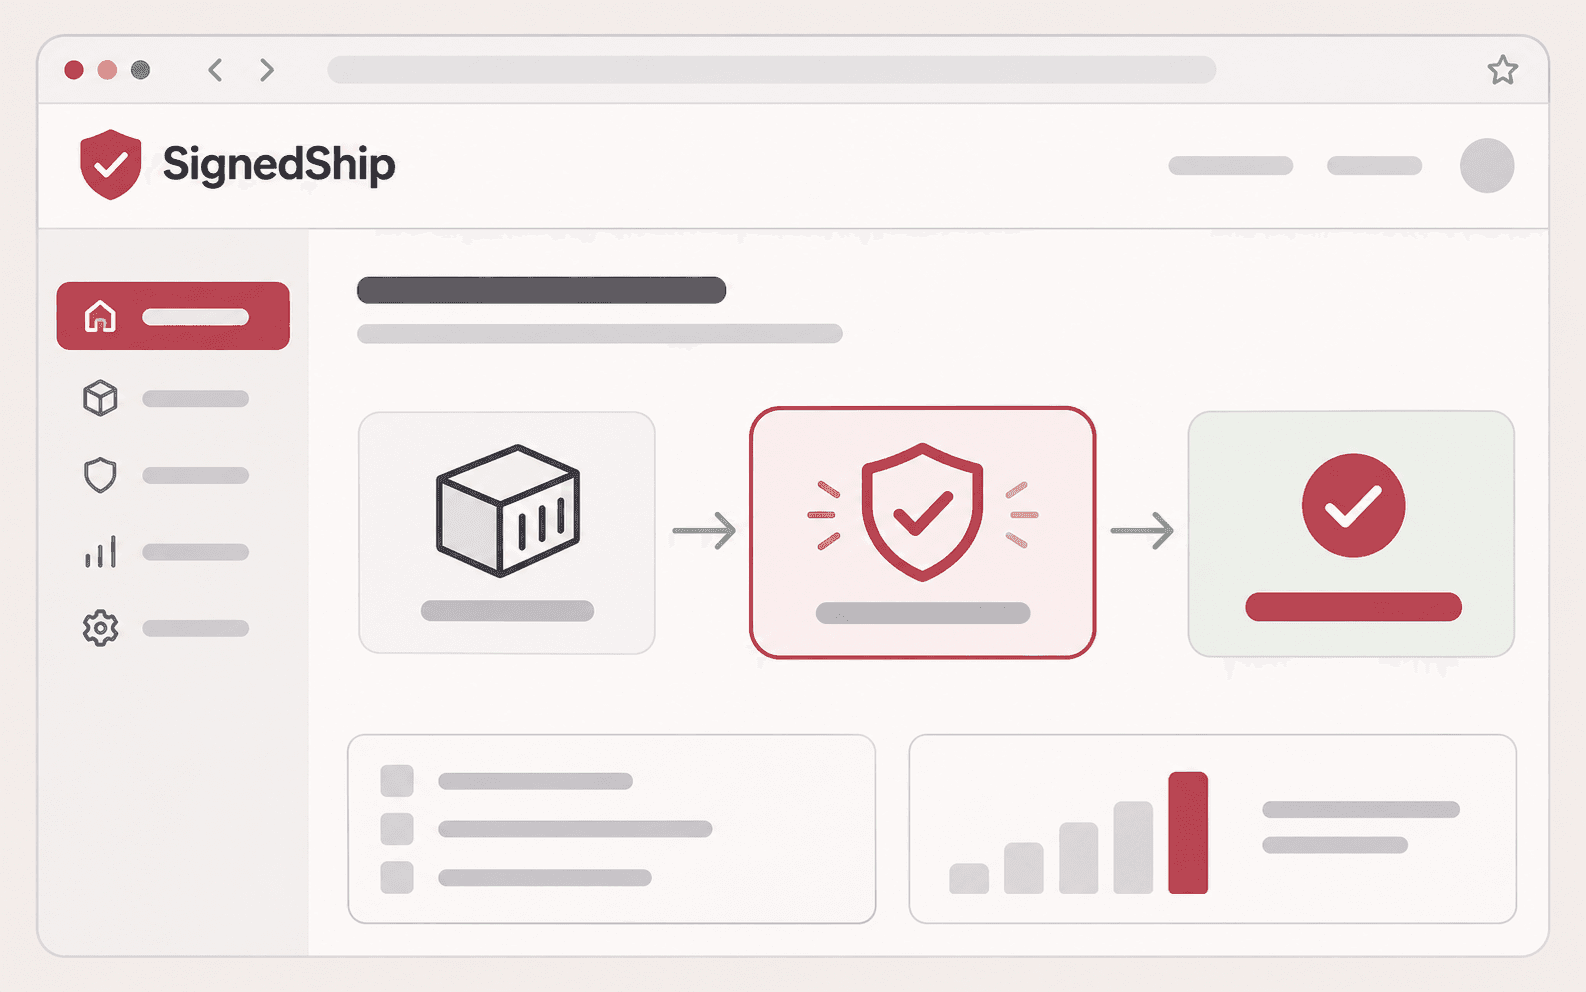
20 / DevSecOps and AppSec
SignedShip
Require signed container images before deployment.
In planningDiscuss this idea
Concept brief — not yet built. This is a proposed project idea, not completed client work or an existing Develiorate product.
01 / The problem
Why it matters
Unsigned or tampered container images can reach production without anyone noticing.
Who it is for
Teams deploying containers
02 / First release
A focused first version
- 01Verify image signatures at deploy time
- 02Clear policy for trusted signers
- 03Readable failure reasons